Xen XSA-523 Lets Guest VMs Read Dom0 Memory
XSA-523 (CVE-2026-102703/102704): grant-copy cache bug lets a guest R/W other domains including Dom0. Claude found it; patch and reboot.
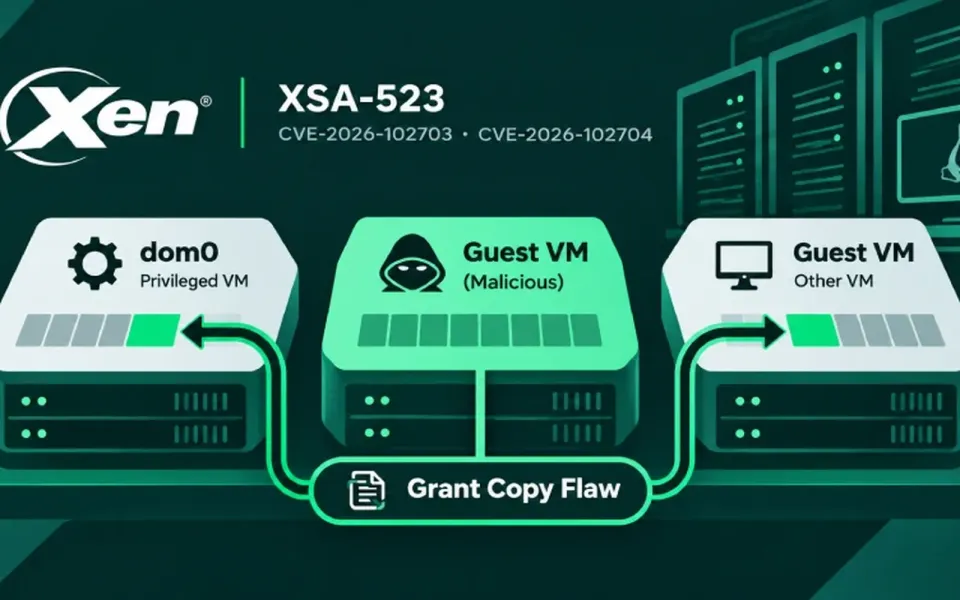
Two fresh Xen bugs let a malicious guest VM read and write memory belonging to other guests — including Dom0, the privileged management domain. The find came from Anthropic's Claude, and there is no workaround besides patching and rebooting.
What happened
On November 3 the Xen Project published XSA-523, tracking CVE-2026-102703 and CVE-2026-102704. Both sit in grant-copy, the path Xen uses to move data between VMs. For speed, Xen caches permission checks when a batch of copies hits adjacent ranges in the same page. In some cases it failed to re-validate that cache: frame numbers and grant references could get mixed up, and a misplaced check let frame-number copies touch memory they should not. Impact, in Xen's own words: a malicious guest can read and write arbitrary memory belonging to other domains, including Dom0.
Every Xen release from 4.6 onward is vulnerable; 4.5 and earlier are not. Xen shipped patches for xen-unstable through 4.19.x and for 4.18.x–4.17.x. There is no patch listed for 4.6–4.16 (4.16's support already ended). Credits go to Anthropic for discovering the issue with Claude, Stephan Lipp of Ada Logics for validation, and a later independent report from CodeAnt's AI security team. The Hacker News covered the advisory the same day; @TheHackersNews summarized it on X.
Downstream: XCP-ng 8.3 shipped xen-4.17.7-4.2.xcpng8.3 on November 3 and calls for a host reboot. Qubes OS 4.3 has Xen 4.19.6-3 packages for Dom0 (restart Dom0; Anti Evil Maid users must reseal). Vates rates the XCP-ng impact Critical: one compromised guest can break isolation and take the host.
Why it matters
Grant-copy bugs are the classic "hypervisor isolation is only as good as the edge cases" story. Dom0 compromise is game over for every guest on that box. The AI angle is interesting for a different reason: Claude found a real, shippable advisory that humans then validated — same pattern as other recent model-assisted reports, and a reminder that AI-found bugs still need the boring ops work of patching clusters. If you already rotate keys after cloud incidents like the ones in our Railway breach key checklist, treat this the same way for any Xen-backed fleet.
What to do
- Xen source / custom builds: apply the XSA-523 patch set for your branch, then reboot hosts so the new hypervisor is live.
- XCP-ng 8.3: install the November 3 Xen update and reboot each host.
- Qubes OS 4.3: install the Xen Dom0 packages when they reach you (security-testing first, then stable), restart Dom0, reseal Anti Evil Maid if you use it.
- Citrix / other Xen products: watch their own advisories; anything still on 4.6–4.16 with no vendor backport is stuck until you upgrade the platform.
- There is no mitigation short of patching. Prefer not to park untrusted guests on unpatched hosts.



Comments ()